Skip to content
#explainable ai Review Open access

A Threat Modeling Prioritization and Automation Framework for Composable Architectures

Sep 2026 · Future Internet · 0 citations · 41 references
Information and Cyber Security

TL;DR

A snapshot of the literature review of the threat modeling for composable architectures is offered, why automation is difficult in this context is shown, and an automation framework to allocate scarce resources according to risk exposure to composable architecture components is proposed.

Abstract

Organizations face escalating cyber risk, expanding attack surfaces, increasingly automated adversaries, and constrained security resources. Organizations are looking for practical mechanisms to improve security resilience by transforming threat modeling from a periodic design activity into a continuous, evidence-driven decision process. This paper offers a snapshot of the literature review of the threat modeling for composable architectures, shows why automation is difficult in this context, and proposes an automation framework to allocate scarce resources according to risk exposure to composable architecture components, where applications, services, identities, data flows, and autonomous agents are assembled and reconfigured across distributed environments. Composable architecture shows in an amplified way the gap between the static and dynamic security approaches, and our proposal helps to define the attributes needed for setting automation boundaries at the service level for risk prioritization based on threat modeling for security remediation actions. The conceptual framework integrates Zero Trust principles, control-effectiveness measurement, and human-in-the-loop governance and examines how automation with artificial intelligence changes the threat landscape by introducing risks that are difficult to measure and fast-changing. The results show that automation should be controlled with defined boundaries explained through measurable attributes for transparent decisions. It also proposes that AI should not replace expert judgement; rather, it should augment security teams by improving information quality, revealing hidden dependencies, supporting adaptive prioritization under uncertainty, and enabling resilience-oriented investment decisions for composable, distributed, and increasingly autonomous systems.

Read PDF

Similar papers

Book Open access Oct 2026

Metamodel-Based Generation of Security Models from Structured Cyber Threat Intelligence

This paper presents a prototype approach that transforms publicly available attack knowledge from sources such as MITRE ATT&CK and MITRE EMB3D into instances of the Security Abstraction Model (SAM), a domain-specific security metamodel, and outlines future research directions toward continuous, data-driven cybersecurit...

Alexander Fischer, Ramin Tavakoli Kolagari · 0 citations
#artificial intelligence Review Sep 2026

Trustworthy Agentic AI: A Comprehensive Cybersecurity and Systems Survey on Threat Landscapes, Defense Architectures, and Open Challenges

This survey systematically analyze threat surfaces across intra-execution loops and interaction planes, formulate a multi-layered zero-trust defense-in-depth architecture integrating Dual-LLM isolation, Capability-Based Access Control, kernel eBPF probes, and sandboxed runtimes, and map technical controls to internatio...

Seyedakbar Mostafavi · 0 citations
Preprint Aug 2026

Agentic AI Cybersecurity Framework

An Agentic AI Cybersecurity Framework (AACF) is introduced designed to enable autonomous, goal-driven, and adaptive cyber defense operations and provides a foundation for developing resilient, scalable, and intelligent defense infrastructures.

Victor R. Kebande · 0 citations
Open access Aug 2026

DISTRIBUTED AI-ASSISTED RISK ASSESSMENT FOR ZERO-TRUST MICROSERVICES: A TAXONOMY AND CONCEPTUAL FRAMEWORK

This paper proposes a conceptual framework for distributed, AI-assisted risk assessment designed to address the gap between conventional vulnerability management and distributed systems, and outlines key open challenges— data, robustness, performance, consistency, explainability, and evaluation.

Daoquan Zhou, Xiong-Sheng Yi · 0 citations
#artificial intelligence Review Sep 2026

Connecting the Dots in Agentic AI Security: A Cross-Dimensional Threat Taxonomy, Evaluation Maturity, and Open Challenges

Evidence concentrates on prompt/reasoning, memory, and tool-mediated attacks, predominantly in single-agent settings, within the selected studies, to guide more systematic, architecture-aware, and reproducible security evaluation of agentic AI.

Heewon Baek, Alsharif Abuadbba, Kristen Moore et al. · 0 citations
Open access Aug 2026

TOWARD SDN-NATIVE CYBERSECURITY: UNIFIED THREAT MODELING, FORMAL ASSURANCE, BEHAVIORAL DETECTION, AND MULTI-CONTROLLER RESILIENCE

This study designs and analytically evaluates an SDN-native cybersecurity integration contract that unifies: a multidimensional threat model; invariant-based preventive assurance; governed hybrid detection; security-aware multi-controller resilience; ATT&CK informed traceability; and controlled learning.

Oumar Y. Maïga, Moussa Koita, I. Traoré et al. · 0 citations

Related blog posts

Microsoft Research Blog Nov 16, 2026

TokenEconomizer: Learning from Experience to Make AI Coding Agents More Efficient

AI coding agents are increasingly help developers fix bugs and build features largely on their own, but every interaction with their models consumes tokens. In each session, an agent sends instructions, tool descriptions, and session history to its model. Most efforts to reduce this cost focus on individual tasks. Yet developers return to the same […] The post TokenEconomizer: Learning from Experience to Make AI Coding Agents More Efficient appeared first on Microsoft Research.

GPT-Lab Nov 13, 2026

TenderIntell at ICSOB 2026: Three Days in Gothenburg

At ICSOB 2026 in Gothenburg, we presented TenderIntell, our work on multi-agent support for tendering. This post looks back at the conference, the idea behind a panel of three AI reviewers who score each proposal independently, and why evaluating agents reliably is the question we keep coming back to. The post TenderIntell at ICSOB 2026: Three Days in Gothenburg appeared first on GPT-Lab.

MIT News · Artificial Intelligence Nov 13, 2026

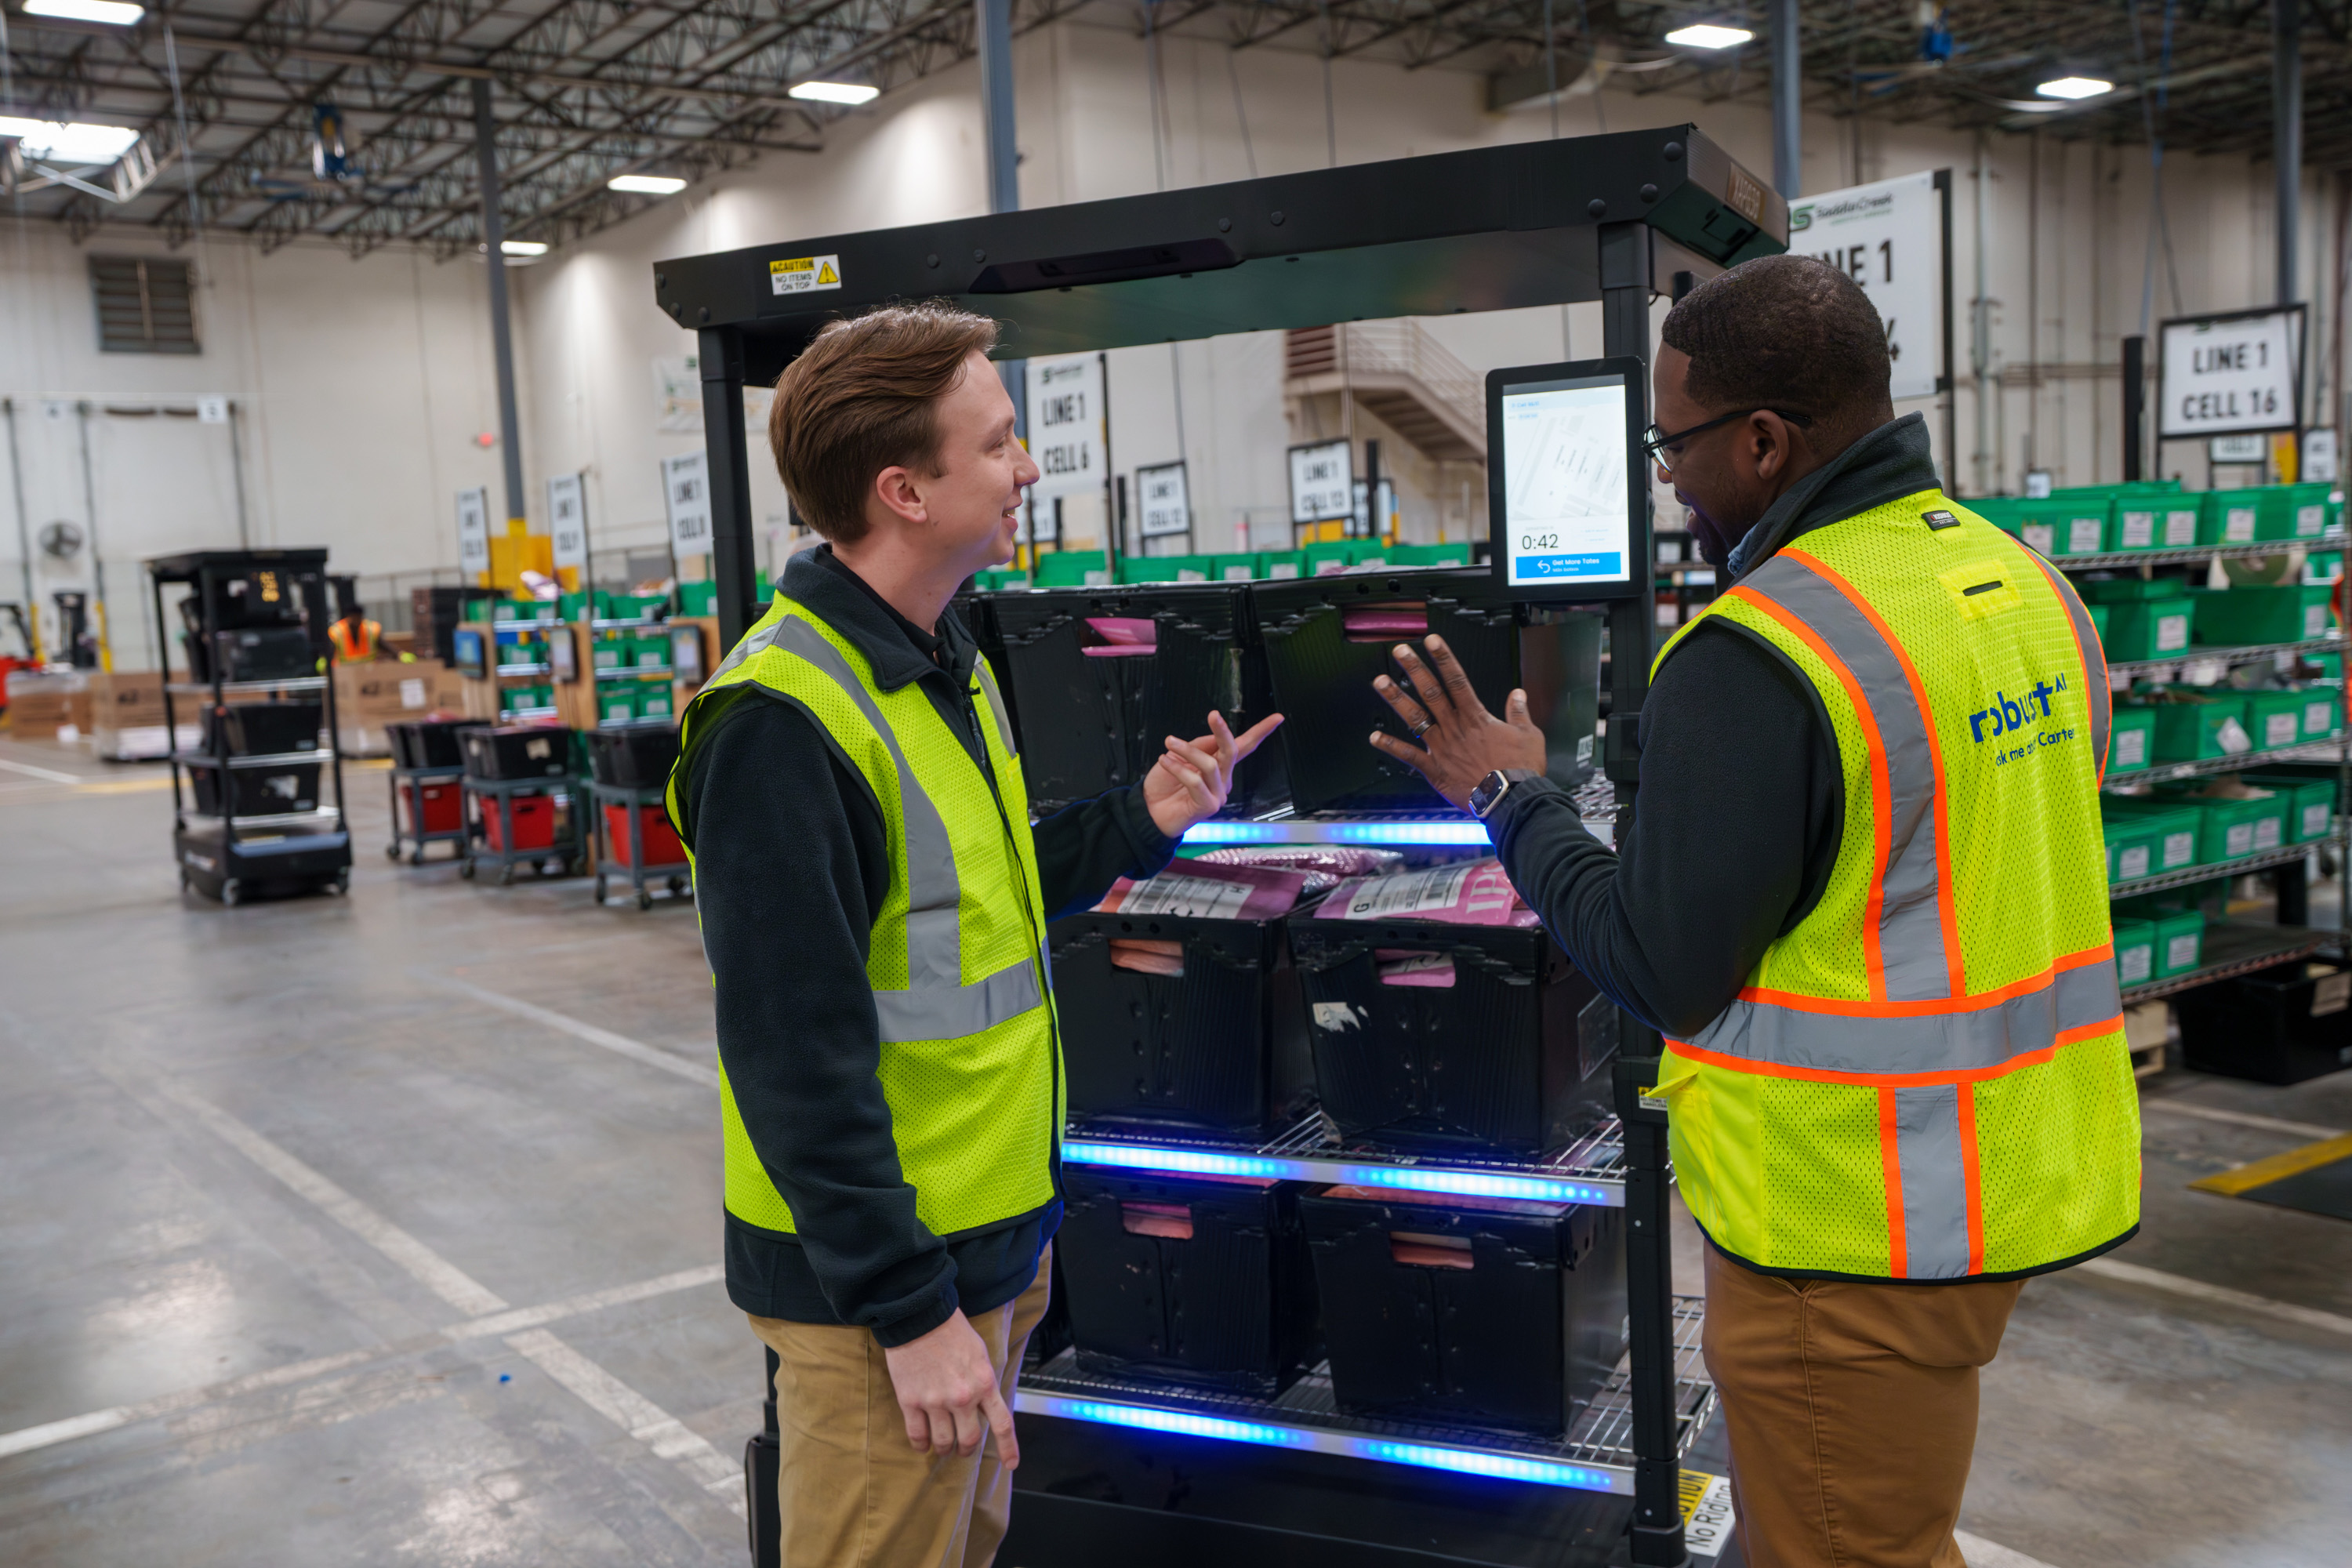
Helping robots fit into the human workplace

Founded by Anthony Jules ’92, SM ’92 and Professor Emeritus Rodney Brooks, Robust AI’s robots are designed to collaborate with humans in factories and warehouses.

We use cookies to run the site and, with your consent, for analytics and to show ads. See our Cookie Policy.